Graphic representing the Initial Trust Plan checklist for data protection in multi-academy trusts and schools.

Multi academy trusts, federations and groups of schools face a particular data protection challenge. Each school handles personal data every day, but accountability sits with the trust. The Initial Trust Plan is a checklist that gives your central team a clear, high-level picture of where the trust stands and what needs attention first.

This article is part of our Governance Week series. It brings together everything you need to know about the Initial Trust Plan: what it covers, who should own it, how it fits with the ICO Accountability Framework and how to get started.
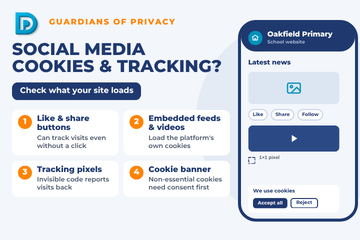
Illustration depicting social media icons and digital cookies, symbolizing online tracking and data privacy on a school website.

Your school website is probably the most visited "front door" you have. Parents check it for term dates, prospective families browse it before an open evening, and pupils use it to find homework links. If that website carries a Facebook "Like" button, an embedded Instagram feed, a YouTube video or a tracking pixel, some of those visitors are being tracked by social media platforms before they have clicked on anything.

Visual representation of the DPE Governance Lead role, highlighting leadership and strategic oversight.

We recommend every multi academy trust we work with having a named Data Protection Governance Lead. We explain what the role involves, how it differs from the Data Protection Officer (DPO) and  the Data Protection Champion, the training we expect, and the new resources available to help you.

Data protection champion serving as a central point of contact for data security and privacy.

So, you've been asked to be the data protection champion/lead in your organisation!  We explain what that  role involves, how it works with Data Protection Education (DPE) as your Data Protection Officer (DPO), and the new resources we've added to help you.

Halloween-themed graphic marking the end of Cyber Month, symbolizing resilience against cyber attacks and disruptions.

This series opened by making the case that cyber security matters. Cyber resilience is an organisation's ability to anticipate, withstand, recover from and adapt to cyber attacks and disruptions while continuing to deliver essential business operations.

Data recovery professional testing a complex backup system to ensure critical data protection and business continuity.

A backup you’ve never tested isn’t a backup, it’s a hope. The only way to know a recovery plan actually works is to have tried it before the day it matters.

Old electronic devices like laptops and printers, symbolizing e-waste and the need for secure data

Most of this series has been about what happens on screen. This one’s about what happens when the screen is switched off: the old laptop in a cupboard waiting to be “sorted,” the printer in the corner nobody’s logged into in years, the server room door that’s been propped open since this morning’s delivery.

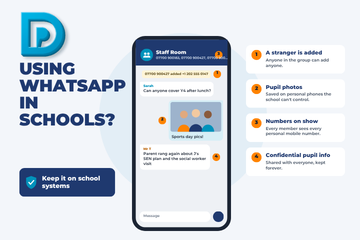
WhatsApp logo on a smartphone screen, representing its use for school communication and data protection concerns.

WhatsApp is one of the most common questions we're asked about. Staff want to know whether they can use WhatsApp groups for school messages, and it's easy to see why: it's familiar, free and quick. But using a personal messaging app for school business brings real data protection, safeguarding and security risks. This article sets out those risks, what the ICO and WhatsApp itself say, and what schools and trusts should do instead.

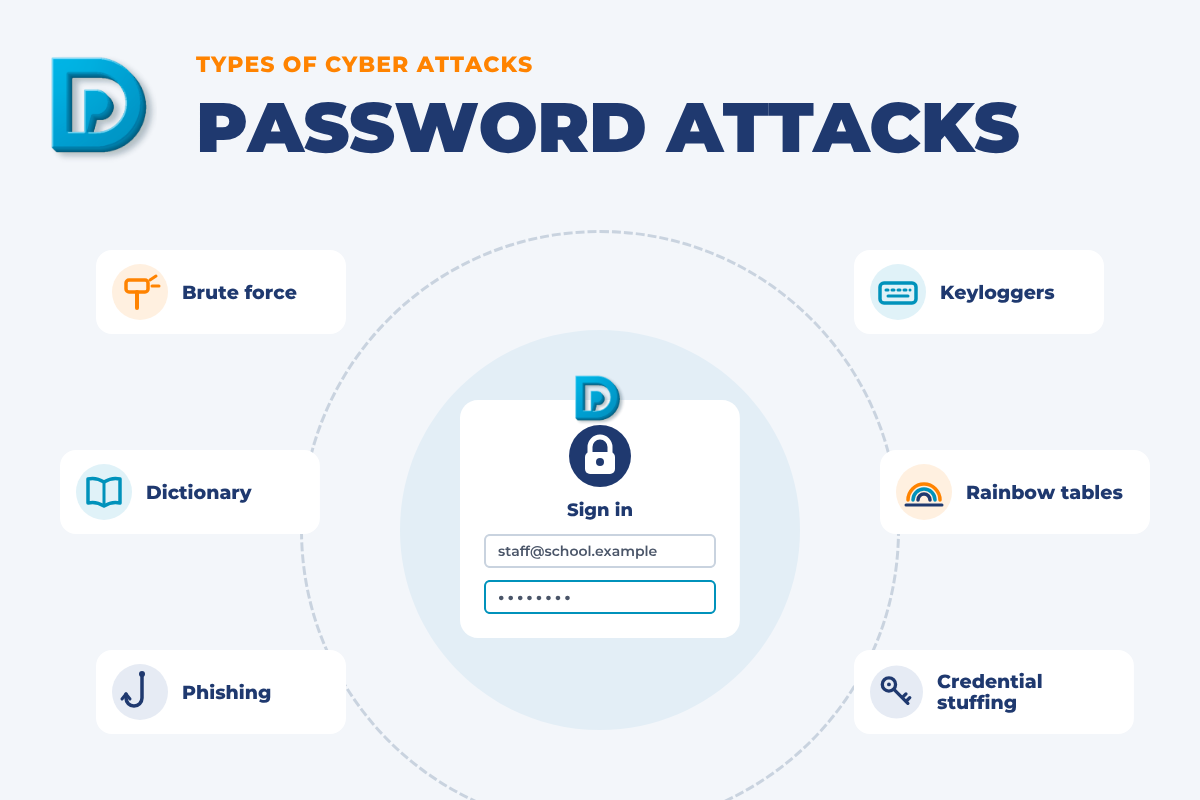
A visual representation of various password attacks, highlighting the vulnerability of online accounts to hackers and cyber threats

Hackers are always finding new ways to break into accounts, and password attacks remain one of the most successful routes into school and trust systems. Password security isn't just an IT job: everyone with a login has a part to play.

Gemini API error (400): * GenerateContentRequest.contents: contents is not specified

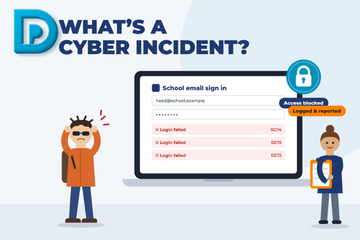
This article explains what a cyber incident is and what you should do if your school or trust experiences one. A cyber incident isn't necessarily a full-blown cyber attack, but it should still go through your reporting and risk management processes.

Calendar showing October 25th, symbolizing a critical deadline for cybersecurity patching and vulnerability management

A single unpatched device rarely causes a breach on its own. It’s the one left running an outdated browser plugin, the printer firmware nobody’s touched in two years, the laptop still on last year’s operating system, sitting quietly until something finds it. Patching is the least exciting item on this list and the one that closes the most doors.

Cyber Career Week banner showing school staff roles and cybersecurity responsibilities.

This week, we’re using “Cyber Career Week”, the name the wider world already knows it by, to look at cyber security through the lens of who’s actually responsible for what in a school or trust. Not generic career-pathway content, but the real division of labour: what each role is accountable for, where the handoffs happen, and where things go wrong when nobody’s sure whose job it was.

Technician Dave working on school IT security during Cyber Career Week in October, ensuring system accountability."

This week, we’re using “Cyber Career Week”, the name the wider world already knows it by, to look at cyber security through the lens of who’s actually responsible for what in a school or trust. Not generic career-pathway content, but the real division of labour: what each role is accountable for, where the handoffs happen, and where things go wrong when nobody’s sure whose job it was.

Cyber security roles and responsibilities in a school during National Cyber Security Career Week.

This week is National Cyber Security Career Week, and while most content for it focuses on getting new people into the profession, we’re taking a different angle. Cyber security in a school or trust isn’t a job for one person or one department; it’s a set of responsibilities spread across several roles, each with a different part to play.

Cyber security responsibilities in schools and trusts, highlighting shared roles for protection.

This week is National Cyber Security Career Week,  and while most content for it focuses on getting new people into the profession, we’re taking a different angle. Cyber security in a school or trust isn’t a job for one person or one department; it’s a set of responsibilities spread across several roles, each with a different part to play.

Cyber security week graphic illustrating shared responsibilities across school roles, from Headteacher to staff.

This week is National Cyber Security Career Week, and while most content for it focuses on getting new people into the profession, we're taking a different angle. Cyber security in a school or trust isn't a job for one person or one department; it's a set of responsibilities spread across several roles, each with a different part to play.

Cyber security responsibilities shared across various roles in a school or educational trust.

This week is National Cyber Security Career Week, and while most content for it focuses on getting new people into the profession, we're taking a different angle. Cyber security in a school or trust isn't a job for one person or one department; it's a set of responsibilities spread across several roles, each with a different part to play.

Digital shield representing online filtering and monitoring protecting users from harmful content and cyber threats for child safety.

Filtering and monitoring sit either side of the same boundary. Filtering is preventative, it stops users reaching illegal, inappropriate, or harmful content before they ever see it. Monitoring is reactive, it watches what's actually happening on your network and devices, so concerning activity doesn't go unnoticed. Together, they're one of the few controls that serve both cyber security and child safeguarding at once.

Digital firewall protecting a network with data connections, representing robust perimeter and gateway security.

Day 16 looked at access control from the outside in: securing the connection when staff work beyond school walls. Today we go back to the perimeter itself: the firewall every one of those connections has to pass through, and the network behind it. A firewall that's switched on but never reviewed, or a network where one device can talk to everything else, undoes a lot of the good work covered so far this month. Perimeter and gateway security is less glamorous than ransomware or phishing, but it's the layer that decides whether an intrusion stays contained or spreads.

Cybersecurity awareness for remote school staff, securing access outside school walls on 16 October.

Cyber Security Awareness Month has spent the last two days on who has access and how it's controlled inside your school's own walls. But for most schools and trusts today, "inside the walls" is only part of the picture. Staff mark books at home, SLT reply to emails on the train, and admin teams log into finance systems from a kitchen table. Remote working isn't an edge case anymore; it's routine. Which means access control has to work just as hard outside the building as it does inside it.

Cybersecurity graphic illustrating network access control, preventing cyber attackers from compromising school admin accounts and

Every attacker chasing a school network has the same goal once they're in: find an account with more power than it needs. A compromised standard user account is a nuisance. A compromised admin account is a takeover, it can touch every system, every dataset, and every piece of security infrastructure built to stop exactly this. It can probably reset passwords.

Official DfE Data Protection Guidance banner for schools, featuring the new DUAA compliance checklist.

On 14 October 2026 the Department for Education (DfE) replaced the Data (Use and Access) Act chapter of its Data protection in schools guidance with a new, practical DUAA compliance checklist for schools. The previous chapter told schools to review their procedures and promised more information "in due course". This is that information: eight themed checklists setting out what changed and what schools are expected to do about it.

Cyber security policies and acceptable use guidelines for school IT resources, protecting staff and pupils.

Cyber security policies and procedures set out clear rules, guidelines and processes for how information is handled across your school or trust. Done well, they're not a compliance exercise, they're the blueprint that reduces human error and makes accountability possible, because everyone knows what's expected before something goes wrong, not after.

Digital padlock protecting sensitive data, symbolizing strong access control against phishing and ransomware.

Over the past two weeks, we've covered how attackers get in:  phishing, deepfakes, ransomware, and what to do when they do. Access control is about the layer that decides whether any of that actually works: even a perfectly crafted phishing email or a stolen password is useless to an attacker if the account behind it is properly protected. Today we look at the single most effective access control measure available, where it still falls short, and what's changing.

Preventing Ransomware | October 12

The NCSC advises: "there's no way to completely protect your organisation against malware infection." That's not a reason to give up, it's the reason defence-in-depth exists. Instead of relying on one control to stop everything, you build multiple layers, so that if one fails, the next one catches it, and if an attacker does get in, the damage is contained and recovery is fast.

  1. The Reality of Ransomware | October 11
  2. Cyber Posture: From reactive panic to proactive preparedness | October 10
  3. Normalising Immediate Incident Reporting | October 9
  4. Phishing: AI-Crafted Bait | October 8
  5. AI Deep Fakes: Synthetic Video & Visual Verification | October 7
  6. AI Deep Fakes: Spotting Audio & Voice Cloning Scams | October 6
  7. Cyber Responsibilities - We're all in this together! | October 5
  8. Data Protection & DPIAs – Safeguarding Pupil & Staff Data | October 3
  9. Behavioural Change – From Passive Training to Active Vigilance | October 2
  10. Welcome to Cyber Security Month 2026 – Don't Make It Easy For Them! | October 1
  11. Bromcom SSO Data Breach | DPE
  12. The ICO is Changing Behind the Scenes: What Schools Need to Know
  13. Handling Subject Access Requests (SARs) and Coerced Consent: Guidance for Schools | DPE
  14. When the Annual Training Cycle Doesn't Fit: Data Protection for Support, Supply and Short-Term Staff
  15. What is Making the Rounds? What happens during a data walk?
  16. AI In Schools: Six Pillars for Getting it Right | Serious Privacy
  17. Knowledge Bank Updates: What's New
  18. Back to School: Your Data Protection Checklist for the New Academic Year
  19. New e-learning for 2026: Data Protection Training
  20. Payroll Fraud Alert: Schools Urged to Secure Staff Accounts After Thames Valley Attacks
  21. A Risk-Led Order for the DfE Digital Standards: Step by step guidance
  22. Staying Ahead: Why We've Updated Our AI Policy Template
  23. New Course: Keeping Children Safe in Education (KCSIE 2026)
  24. The DfE Cyber Attack: What Schools Should Look Out For Next Term
  25. Sharing Pupil Allergy Information Safely in Schools: A Practical Guidance & SSCIP Framework |DPE
  26. DfE Guidance: Choosing an MIS | The DPO lens on the commercial guidance
  27. Academy Trust Handbook 2026: What Data Protection Leads and Governors Need to Know
  28. DfE Procurement Risk Guide: Due Diligence and Data Protection for Trusts | DPE
  29. DfE Data Protection Advice for Schools
  30. KCSIE 2026 Data Protection Changes: What Schools Need to Know
  31. Important Guidance for Schools: Record Retention and the Statutory Independent Inquiry into Grooming Gangs
  32. DfE Cyber Security Standards for Schools: June 2026 Update | DPE
  33. ICO EdTech Audit 2025: Key Findings for Schools | DPE
  34. DfE updates Data Protection in Schools guidance: what schools need to know
  35. The DSL’s Guide to Filtering and Monitoring
  36. Cyber Attack : LockBit 5.0 Targets a Primary School
  37. Human Error and High Stakes: What the Horizon Academy Trust Incident Teaches Us About School Data Breaches
  38. We’re Bringing It Back: Our Data Protection Conference Returns
  39. When Cyber Risk Becomes Reality: Lessons from the Powys School Attack
  40. Reducing risk on World Environment Day and Beyond
  41. Navigating the Future: 2026 Privacy Updates, Data Access, and Student Wellbeing
  42. What the Data (Use and Access) Act Means for Schools
  43. Can you use AI safely in schools?
  44. Guardians of Privacy: Social Media, Privacy, Children and the AI Threat
  45. What School Leaders Need to Know About the DfE's New Cyber Security Hub
  46. A guide to multi-factor authentication
  47. World Password Day
  48. The Cyber Security Breaches Survey 2025/2026 - Key Advice for Schools
  49. The 2026 Mandate: Navigating the Children’s Wellbeing and Schools Act.
  50. Visitor Management: A Guide for Schools
  51. Under surveillance: Why your organisation's CCTV might not be compliant
  52. Update to the DfE Digital Cyber Security Standards for Schools and Colleges
  53. Wireless Network Standards for Schools & Colleges: What's New?
  54. How were schools and pupils affected by the C2K cyber attack?
  55. World Backup Day: Backups - Your Safety Net
  56. School Cyber Attack: St Anne's Catholic School
  57. Volunteer Acceptable Use Policy & Agreement
  58. Handling Subject Access Requests (SARs) - at the end of term
  59. Holiday Cheer or Cyber Fear? : Essential Pre-holiday Checks
  60. How should schools manage paper archives?
  61. Navigating the Redaction Divide: SAR or PEX?
  62. What is the Stryker cyber attack and why should schools be wary?
  63. Records Management Toolkit: Where do I start with records management?
  64. What type of request have you received? SAR? Educational Record? Or FOI?
  65. SAR Extension Template
  66. Leavers' Memorabilia
  67. Sharing photos on World Book Day: Privacy considerations
  68. Make sure DPE is your registered DPO with the ICO
  69. Supplier Due Diligence Step by Step: Are you sharing personal data with a third party organisation?
  70. Time to kick-start your Clear Desk and Screen policy?
  71. Are Governors the Frontline of Cyber Security? (February 12th is Governors Awareness Day)
  72. DPE Webinar Schedule
  73. The Data (Use and Access) Act: What does it mean for schools and MATs?
  74. Podcast Episode 2: Data (Use and Access) Act - what does it mean for schools?
  75. The Danger of the 'Data Dump': Why more information isn't always better!
  76. Cyber Alert: Surrey and Sussex Schools Targeted by Phishing and Ransomware Attacks
  77. Introducing our new Recording and Transcription Policy
  78. Parents and students covertly recording conversations
  79. New DfE AI Standards
  80. Is your IT Support Provider Compliant?
  81. The Government Cyber Action Plan
  82. School Cyber Attack: Higham Lane School Hit by Major Cyber Attack: Campus Remains Closed
  83. Shareable Snippet: Office Security Best Practices for the Holidays
  84. CCTV Policy update: retention
  85. Shareable Snippet: Be Cyber Ready
  86. Shareable Snippet: Confidential waste
  87. What does the technology in schools survey tell us?
  88. Four London councils hit by cyber attacks - Hackney, Westminster, Kensington & Chelsea, and Hammersmith & Fulham
  89. IT Support Standards for Schools and Colleges Guidance (DfE Digital Standards)
  90. Sharing information to safeguard children and young people in the education sector in the UK
  91. Is your organisation at risk from Shadow AI?
  92. We've teamed up on a podcast with the Small Business Cyber Security Guy
  93. Time's Ticking: Windows 10 support ends in October 2025!
  94. Nursery Cyber attack
  95. The NCSC Cyber Assessment Framework
  96. Fraud awareness from the DfE
  97. Complaints vs. Data Rights: A Guide
  98. The Classroom's Dark Side: Cyber crime from the Classroom
  99. Data Breach: School sends out names and contact details in a spreadsheet.
  100. September 2025 Policy and Document Updates
  101. KCSIE 2025: Data Protection, AI, and Cyber Security
  102. The Online SCR Data Breach: What You Need to Know
  103. Back to School Basics for Data Protection and Cyber Security Compliance
  104. The Latest Cyber Threat: The "Murky Panda"
  105. Building a Secure School: Using the ICO Accountability Framework to Meet DfE Digital Standards
  106. Why Physical and Data Security Must Go Hand-In-Hand
  107. Digital Safeguarding: DfE announces statutory DfE Digital Standards
  108. Compliance Reporting from the Knowledge Bank
  109. School closes for two days after cyber incident
  110. Social Media Day 2025
  111. How Ofsted looks at AI during inspection and regulation
  112. Podcast Episode 3: Records Management and Retention
  113. Podcast Episode 1 - data protection training for school staff
  114. Preschool Employment tribunal for the use of WhatsApp
  115. Social engineering + impersonation = Fraud ≡ cyber deception
  116. Data Breaches 2025 Report Highlights
  117. Not everyone needs access: The Key to Protecting Sensitive Data
  118. School cyber attack: Outwood Academy, Middlesbrough
  119. Alert: Schools receiving Microsoft File Sharing Phishing Emails
  120. School cyber attack: Framlingham College, Suffolk
  121. West Lothian Schools in Cyber Attack
  122. Getting caught in the Scattered Spider web
  123. A Wake-Up Call for Cyber Vigilance - Danger in the Threat Landscape for Everyone
  124. National Honesty Day: Transparency
  125. FOI Request - BBC News
  126. Social Media and Marketing Guidelines and Training
  127. New Governor Resources
  128. Does stress lead to more data breaches?
  129. Are teachers using AI? 83% say its a time-saver
  130. DfE Digital Standards - narrowing the digital divide
  131. Arbor AI - On By Default
  132. DfE Guidance: Choosing a new MIS
  133. HCRG Care Group data breach
  134. Apple removes its highest level data security tool from UK customers
  135. The Importance of AI literacy and training staff
  136. Short Guide to AI Video
  137. Safer Internet Day, Cyber Security & Data Protection
  138. The Cyber Resilience Championship
  139. The Multiple Dimensions of Supplier Due Diligence
  140. School shares sensitive pupil information as part of an FOI response
  141. Blacon High School Cyber Attack
  142. WhatsApp and FOI's: ICO Warnings
  143. New AI Guidance from the DfE
  144. What the proposed Government legislative proposal around cyber crime means
  145. ICO report on AI tools in recruitment
  146. DfE update to record keeping and management
  147. Update to data sharing for school immunisation programmes
  148. Early Years Settings and Cyber Security
  149. SLT Digital Lead Profile
  150. The role of governors in cyber security and data protection
  151. Navigating Privacy at the End of Term , Special Occasions and End of Year
  152. Effectively communicating during a cyber incident
  153. Contracts Register
  154. South East Technological University has experienced a cyber incident
  155. Safeguarding Identity in Microsoft 365: Protecting the UK Education Sector Against Cyber Threats
  156. DfE Digital Standards Autumn Update
  157. The importance of knowing how to access your CCTV footage!
  158. Cyber Attack on a Special School
  159. Stealing children's data
  160. What is dark data? (and why does it matter?)
  161. Ofqual highlights the value of cyber security training in schools
  162. Searching for data when you receive a Subject Access Request
  163. Fylde Coast Academy Trust Cyber Attack This Week
  164. Calling all IT leads in schools and mult academy trusts!
  165. Ransomware cyber attack on a school in Bromley
  166. Join Our Social Media Family!
  167. School hit by Cyber Attack
  168. Cyber Security Best Practice Area
  169. DfE Digital Standards for Schools and Colleges Tracker
  170. New Policies, Documents, Letters and Posters page
  171. Schools and Trusts Best Practice Area
  172. The DPE Retention Schedule
  173. ESFA Cyber Essentials Requirement for Colleges from 2024/2025
  174. ICO Reprimands a School
  175. How does the recent global IT outage affect me?
  176. King's speech introduces new bills in relation to cyber security, smart data and digital information
  177. Out of date technology
  178. Data Retention and the Pupil File
  179. Have you assigned your SLT Digital Lead yet?
  180. Getting Started with AI (Artificial Intelligence)
  181. Cyber attack on a school during half term
  182. Free short cyber training for staff
  183. The rise of cyber attacks in schools are causing pupils to miss classes
  184. ICO: Learning from the mistakes of others report
  185. Children's mental health data leaked after a cyber attack
  186. Cyber attack on a Trust; the aftermath
  187. School Focus: The Vale Federation | Aylesbury
  188. DfE Dealing with Subject Access Requests (SARs) Guidance
  189. Update to the Guidance on Information Sharing from the DfE
  190. FOI Requests generated by Artificial Intelligence
  191. Social Media Best Practice Area
  192. Lettings Best Practice Area
  193. MFA Bombing - What is it?
  194. Protecting your Social Media Accounts
  195. Product Focus on Checklists : End of Term Checklist
  196. Product Focus on Checklists : Information and Cyber Security
  197. Product Focus on Checklists : Social Media
  198. Cyber Incident Review: The Benefits
  199. Product Focus on Checklists : Lettings
  200. Product Focus on Checklists : Record of Processing
  201. Milk Island: The secret location that allows children to view restricted content on Google Maps
  202. Why Data Should Stay Put: Benefits of Keeping Data in Its Original System
  203. Product Focus on Checklists : Data Retention and Destruction
  204. Product Focus on Checklists : Data Migration
  205. Product Focus on Checklists : Biometrics
  206. Product Focus on Checklists : Supplier Due Diligence
  207. Free Cyber help, advice and training with the Cyber Resilience Centres
  208. The Perils of Paper: The Printing Vulnerability
  209. Product Focus on Checklists : FOI
  210. Product Focus on Checklists : Governors and Data
  211. Product Focus on Checklists : DPIA
  212. Product Focus on Checklists : Site Moves
  213. Product Focus on Checklists : Data Breaches
  214. Product Focus on Checklists : Subject Access Requests
  215. Cyber attack on a University
  216. Product Focus on Checklists : Bring your own device
  217. Product Focus on Checklists : Working out of school/offsite
  218. Cyber Attack on a School
  219. Product Focus on Checklists : Redaction
  220. Major cyber-criminal gang Lockbit brought down by UK Law Enforcement
  221. Why Due Diligence is Important: Fake apps
  222. Product Focus on Checklists : CCTV
  223. Product Focus on Checklists : Clear desk
  224. Product Focus on Checklists : Commitment to compliance
  225. Product Focus on Checklists : Photos and video
  226. Product Focus on Checklists : Passwords
  227. Product Focus on Checklists : Information Classification
  228. Safer Internet Day 2024
  229. Kent Councils Data Breach
  230. Free cyber training for staff
  231. DfE Digital Standards Update
  232. The Mother of all Breaches
  233. ClassCharts Possible Data Breach
  234. Where is your data stored?
  235. IAPP looks at AI privacy risks
  236. If you suspect a financial scam .....
  237. Guardians of Privacy: 16. Social Media Checklist
  238. Guardians of Privacy: 15. Navigating Social Media in Educational Settings Summary
  239. Guardians of Privacy: 14. Social Media and Cyber Bullying
  240. Guardians of Privacy: 13. Social Media, Copyright and Intellectual Property
  241. Guardians of Privacy: 12. Social Media and Going Viral
  242. Guardians of Privacy: 11. Staff Social Media Accounts
  243. Guardians of Privacy: 9. Social Media and Morality
  244. New Resources for Schools from the ICO
  245. Guardians of Privacy: 8. Social Media Policies
  246. Guardians of Privacy: 7. Social Media Data Retention
  247. Guardians of Privacy: 6. Posting Safely
  248. Guardians of Privacy: 5. Social Media and Consent
  249. Guardians of Privacy: 4. Social Media Access Control
  250. Guardians of Privacy: 3. Social Media Channels
  251. Guardians of Privacy: 2. Law and Regulations
  252. Latest ICO Reprimand. Mr. S. Claus, Chief Executive Officer, North Pole Enterprises
  253. Phishing attacks targeting schools - alert from City of London Police
  254. The ICO reprimands a Multi Academy Trust
  255. Guidance for the use of school email and applying email retention in schools
  256. CISA and UK NCSC Announce Joint Guidelines for Secure AI System Development
  257. Data Protection Tips for Early Years Settings
  258. Children's Privacy around the world is a puzzle
  259. Update on Advisory for Rhysida Ransomware
  260. Records Management Best Practice Update
  261. The Crime in a Cyber Attack and a Data Breach
  262. What do I need to redact?
  263. Learning from Data Breaches
  264. Windows 11 security ineffective against attacks on old devices
  265. International Counter Ransomware Initiative 2023 Joint Statement
  266. Google for Education Resources: Helping IT Admins meet DfE digital and technology standards
  267. Top Ten Cyber Security Misconfigurations
  268. Lettings Best Practice and Guidance
  269. ICO Reprimand: company suffered a ransomware attack
  270. The UK Online Safety Bill becomes an Act (Law)
  271. Considerations when migrating to a new MIS
  272. The importance of software updates (PaperCut vulnerability and Rhysida ransomware)
  273. Public bodies and sensitive data
  274. Adding offline bulk training using the Certificates function
  275. Ransomware, extortion and the cyber crime ecosystem
  276. Get a DPE Badge for your website!
  277. ICO: 10 Step guide to sharing information to safeguard children
  278. Cyber Resource: The Cyber Resilience Centre Group
  279. Email and Security: ICO recent guidance
  280. Help after a Cyber Attack/Incident
  281. Social Media Policy
  282. Data Protection and Cyber Security (Inset Day) Training Ideas
  283. Changes to Microsoft Free Licensing for Schools
  284. What to do in the event of a Cyber Attack
  285. Cyber Crime: AI Generated Phishing Attacks
  286. Handling Freedom of Information Requests the right way
  287. Cyber Attack: Exam Boards
  288. VICE SOCIETY - Ransomware attacks on schools
  289. Using Tags if you are a group of organisations in the DPE Knowledge Bank
  290. Where's Harry the Hacker?
  291. Be Cyber Aware: USB Sticks
  292. Cyber Insurance in the Public Sector
  293. Types of Cyber Attacks: DDos Attack (Microsoft DDoS Attack in June)
  294. Cyber Attack: Leytonstone School
  295. The ICO Reprimands a school
  296. Be Cyber Aware: Firewalls
  297. Be Cyber Aware: Cyber attacks and transparency. A no blame culture
  298. Cyber Attack: Dorchester School
  299. Knowledge Bank Role Types: Admin, Staff and Trustee
  300. Be Cyber Aware: Why regular software updates are important
  301. Cyber Attack: Wiltshire School
  302. Keeping your IT systems safe and secure
  303. Types of Cyber Attacks: DDoS Attacks
  304. Types of Cyber Attacks: Phishing
  305. Types of Cyber Attacks: The Insider Threat
  306. Why your data is profitable to cyber criminals
  307. The Changes to Data Protection in the UK
  308. Knowledge Bank Updates
  309. Types of malware and how they are linked to data protection
  310. Striking Data Breach
  311. IPR Protection Email Scam
  312. Windows Server 2012 & 2012 R2 Retirement
  313. How to contact us for support, subject access requests, data breaches and FOI's
  314. YouTube breached child protection laws
  315. How a school fought back after a cyberattack
  316. Types of Cyber Attacks - Credential Stuffing
  317. January Cyber update - How Can Schools Help Prevent Cyber Attacks?
  318. Assigning courses to staff using to-dos
  319. How the Record of Processing Can Help You
  320. Information Security Basics: What are VPN's?
  321. What does a Data Protection Officer Do?
  322. Are you ready for a Data Breach?
  323. Carrying out Supplier Due Diligence
  324. How Long Should You Keep Personal Data For?
  325. The Education sector now at highest risk of cyber attacks
  326. How to Assess your Data Security
  327. Schools Blocked from Using Facial Recognition Systems
  328. The Children's Code
  329. B&H FoI: Racist/religious incidents/bullying
  330. Cyber Attacks
  331. Protocol for Setting Up and Delivery of Online Teaching and Learning
  332. Class Dojo International Data Sharing
  333. Model Publication Scheme: Amendments, Improvements and Updates
  334. Child friendly privacy notices
  335. Transparency
  336. Secure file transfer of files using Royal Mail
  337. Emergency contacts and consent
  338. Key elements of a successful DPIA
  339. FOI Publication Schemes
  340. SHARE: Avoid disinformation online
  341. Best Practice for Managing Photos and Video
  342. New Drip Feeds: Recognise and Respond to Subject Access Request
  343. When to contact the Data Protection Officer?
  344. National child measurement programme
  345. Compliance Manager released
  346. Headteacher fined for breach of data protection legislation
  347. Emails – good practice and minimising the risk of a data breach

Search

Guest Subscription

** If guest, Please enroll your name and email for Subscription

Privacy notice